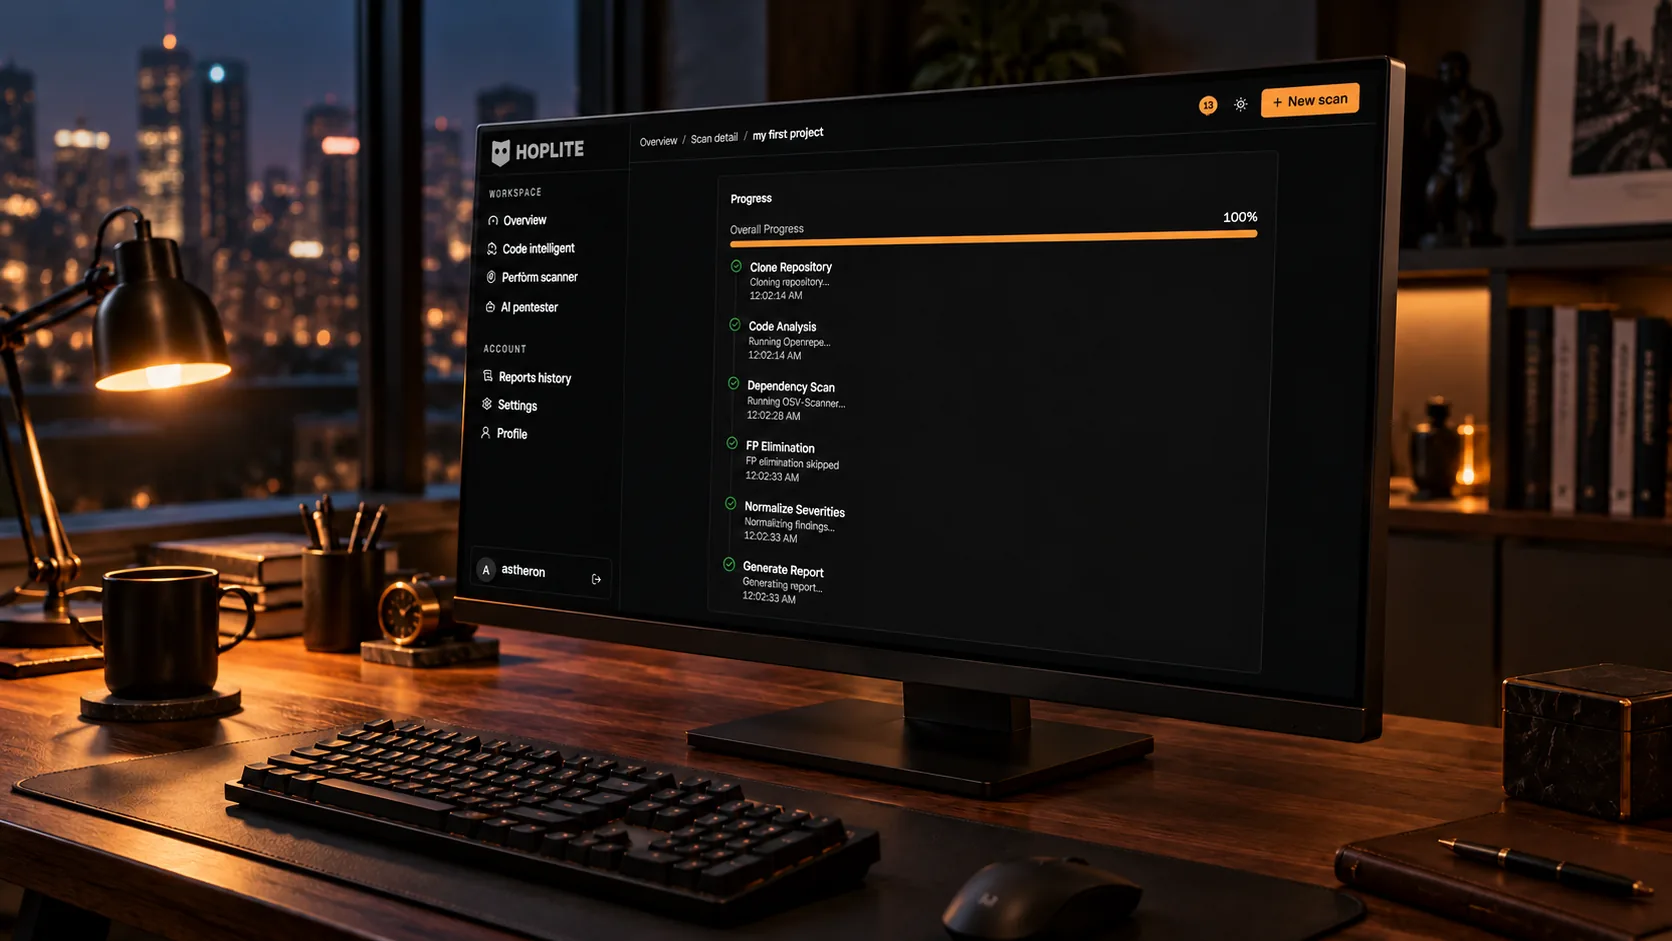
We test applications the way an attacker and a demanding user would. Static analysis and dependency scans run against the source code, dynamic scanners and AI-assisted penetration tests probe the running application, and load tests show where it slows down. The same workflow powers Hoplite, our in-house security product.